Trust & Security
BrightAI is SOC 2 Type II compliant, verified by an independent third-party auditor. Our controls are proven to protect customer data and system integrity over time, not just on the day of an audit.
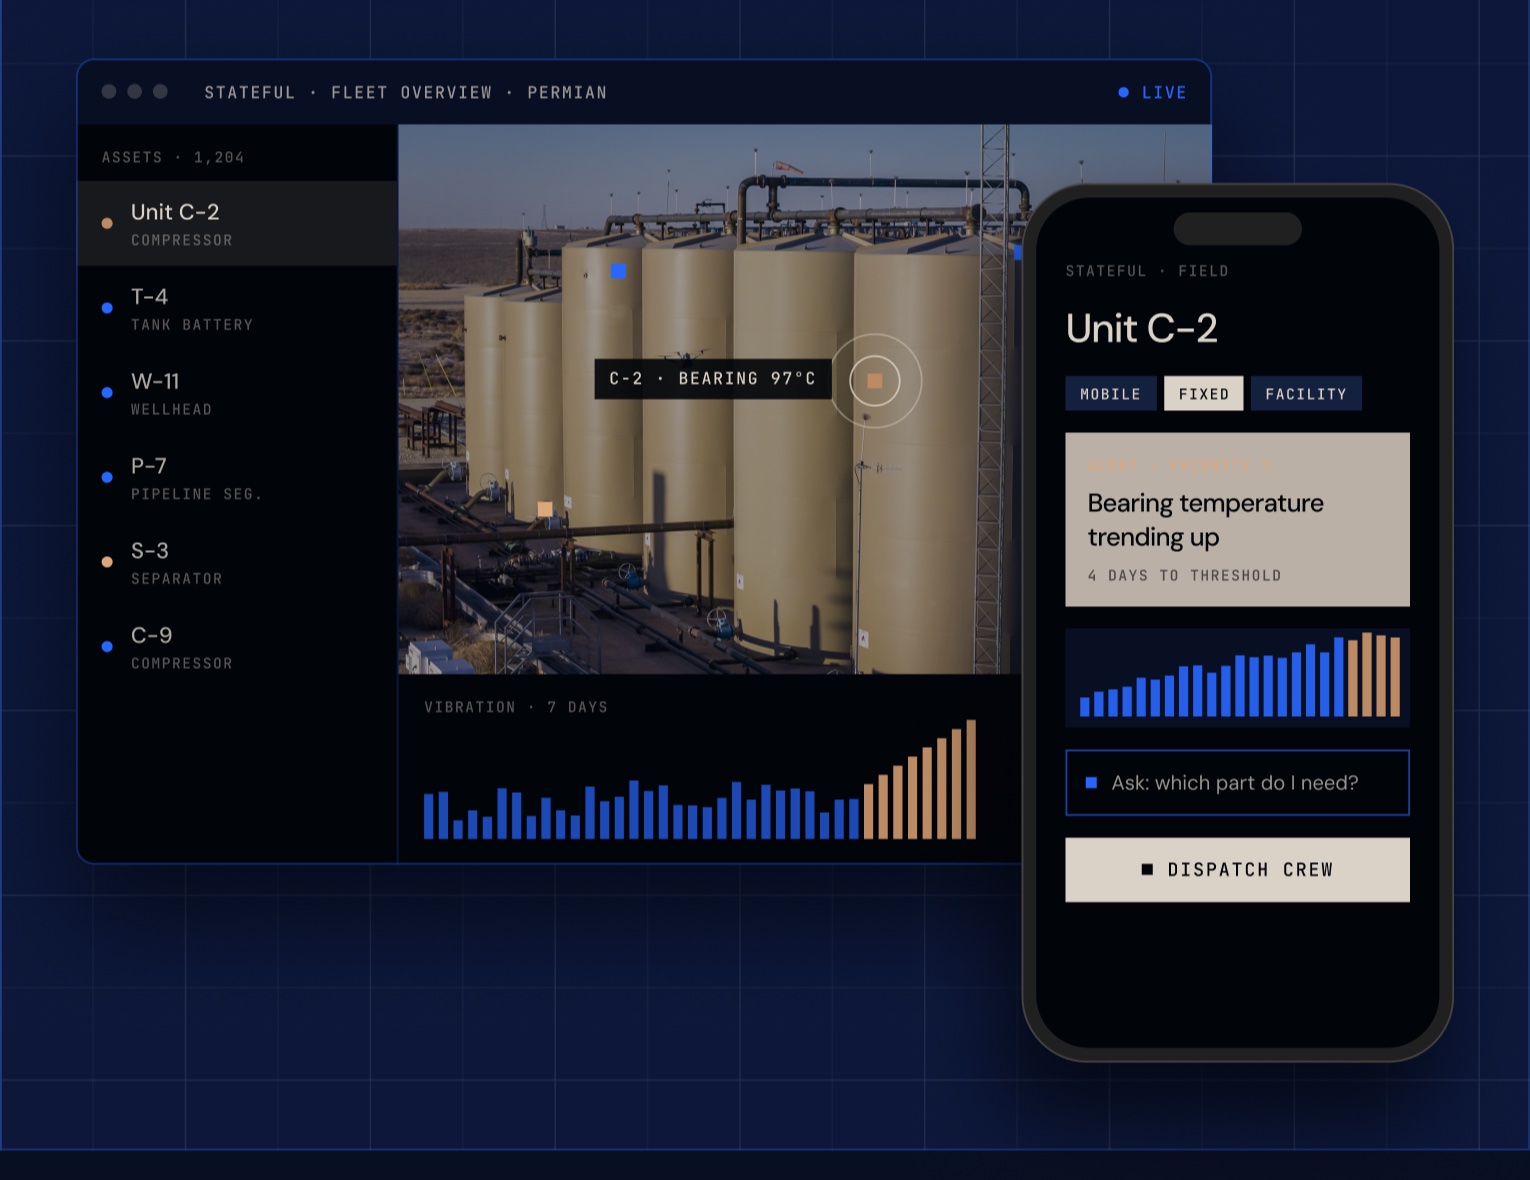
Real detections from live deployments.
SOC 2 Type II
Our platform has been audited against the SOC 2 Trust Services Criteria for security, availability and confidentiality.
01
Protection against unauthorized access.
02
Systems designed for operational reliability.
03
Controlled handling of sensitive data.
Scope of assurance
Scope of assurance
The audit covers the core BrightAI platform. Every in-scope system is evaluated for both design and operating effectiveness.
1
Data ingestion and processing systems
2
Cloud infrastructure and services
3
Identity and access management
4
Monitoring, logging, and operational controls
Operational discipline
Operational discipline
Controls are applied consistently and reviewed regularly.
1
Role-based access and least-privilege enforcement
2
Continuous system monitoring and alerting
3
Comprehensive audit logging of access and actions
4
Defined incident detection and response procedures
Ongoing compliance
Sustained, not one-time
What we maintain